Zero Trust, Zero Hassle: Building a Secure Business Network with Cisco Meraki
Most businesses aren't equipped to implement zero trust from scratch. But if your network runs on Cisco Meraki, you're closer than you think — because Meraki's platform was built with zero trust principles baked in.
Ready to buy Cisco Meraki?
Get a custom quote from our specialists in under 4 hours.
Cybersecurity threats aren't just getting more frequent — they're getting smarter. Ransomware, insider attacks, credential theft, and supply chain breaches have exposed a fundamental flaw in how most businesses built their networks: the assumption that anything inside the perimeter can be trusted. Zero trust was designed to fix that. And Cisco Meraki makes it practical to implement — without a dedicated security team.
"Zero trust is not a product you buy — it's an architecture you build. The goal is simple: never trust, always verify. Every device, every user, every connection gets authenticated before it gets access."
— NIST Special Publication 800-207, Zero Trust Architecture
Most businesses aren't equipped to implement zero trust from scratch. The frameworks are complex, the tooling is enterprise-grade, and the integration work is significant. But if your network runs on Cisco Meraki, you're already closer than you think — because Meraki's platform was built with the core principles of zero trust baked in.
What Zero Trust Actually Means for Your Business
Traditional network security draws a hard line at the firewall. Everything outside is untrusted; everything inside is allowed to communicate freely. That model breaks down the moment an attacker gets past the perimeter — or an employee walks in with an infected laptop.
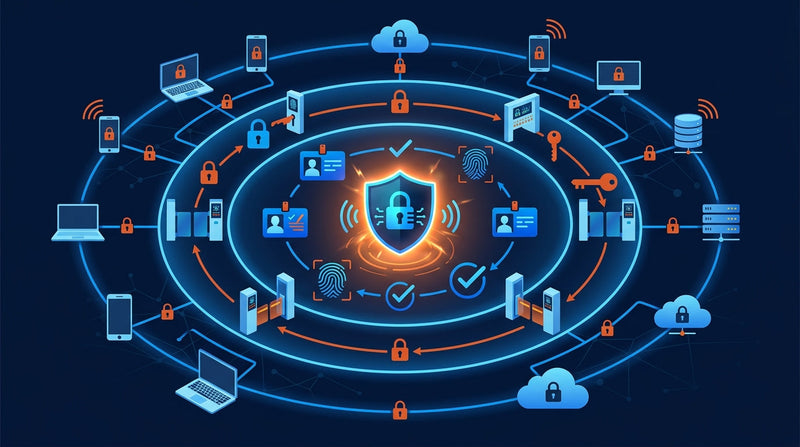
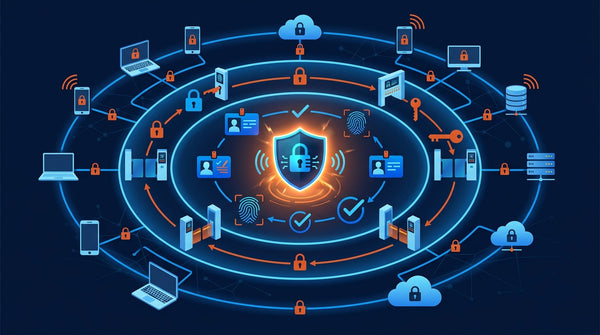
Zero trust replaces the perimeter model with continuous verification. The core rules:
- ✓ Every user must authenticate — regardless of whether they're on-site or remote
- ✓ Every device must be verified — unknown or unmanaged devices get no access
- ✓ Access is least-privilege — users can only reach what they need, not everything on the network
- ✓ Traffic is encrypted end-to-end — even internally, data in motion is protected
- ✓ Everything is logged and monitored — anomalous behavior triggers alerts, not just perimeter breaches
For a small or mid-sized business, that can sound overwhelming. With Meraki, it's a checklist you can actually complete.
Meraki MX: Your Zero Trust Gateway
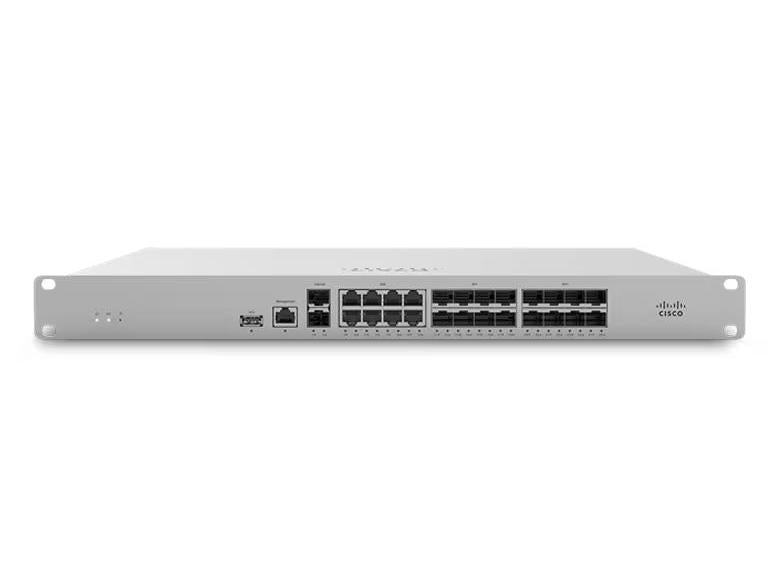
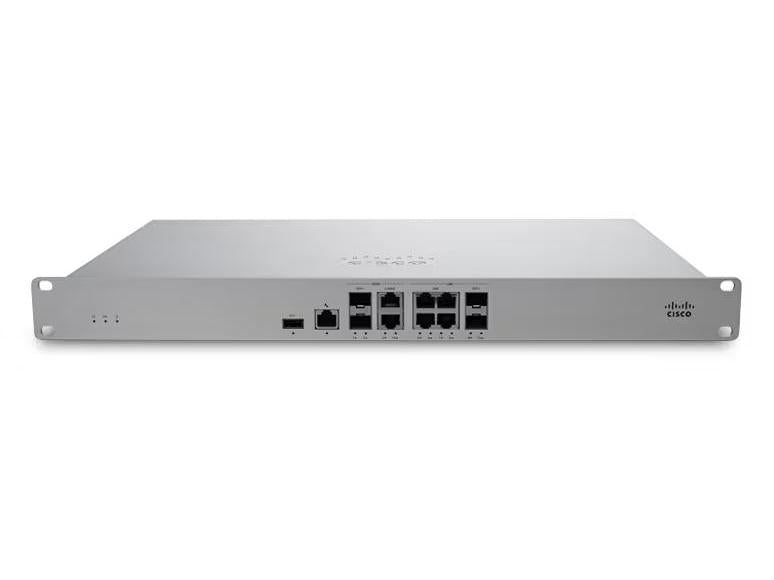
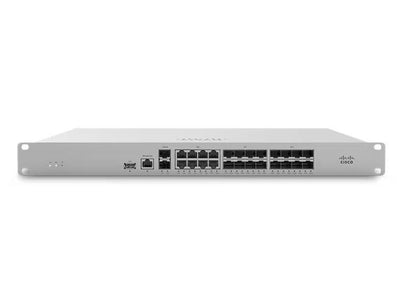
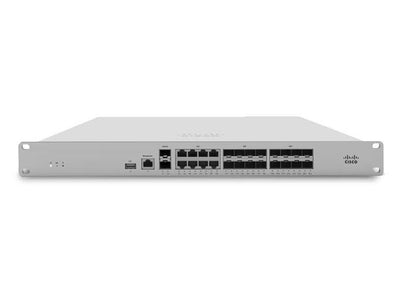
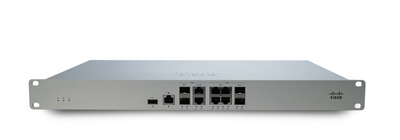
The foundation of zero trust on a Meraki network is the MX security appliance. More than a firewall, the MX is a full next-generation security gateway with:
- ✓ Intrusion detection and prevention (IDS/IPS) — powered by Cisco Talos threat intelligence, updated automatically
- ✓ Advanced Malware Protection (AMP) — identifies and blocks malicious files before they execute
- ✓ Content filtering — blocks known malicious domains at the DNS level, company-wide
- ✓ Identity-based firewall rules — tie access policies to Active Directory or RADIUS groups, not just IP addresses
- ✓ Auto VPN — site-to-site VPN configures in seconds; remote access VPN enforces device posture before connecting
The MX enforces policy at the network edge — but zero trust doesn't stop there.
Network Segmentation: The Zero Trust Foundation
If every device on your network can talk to every other device, a single compromised endpoint can move laterally across your entire environment. This is how ransomware spreads: one infected machine reaches your file server, your backups, and your finance systems before anyone notices.
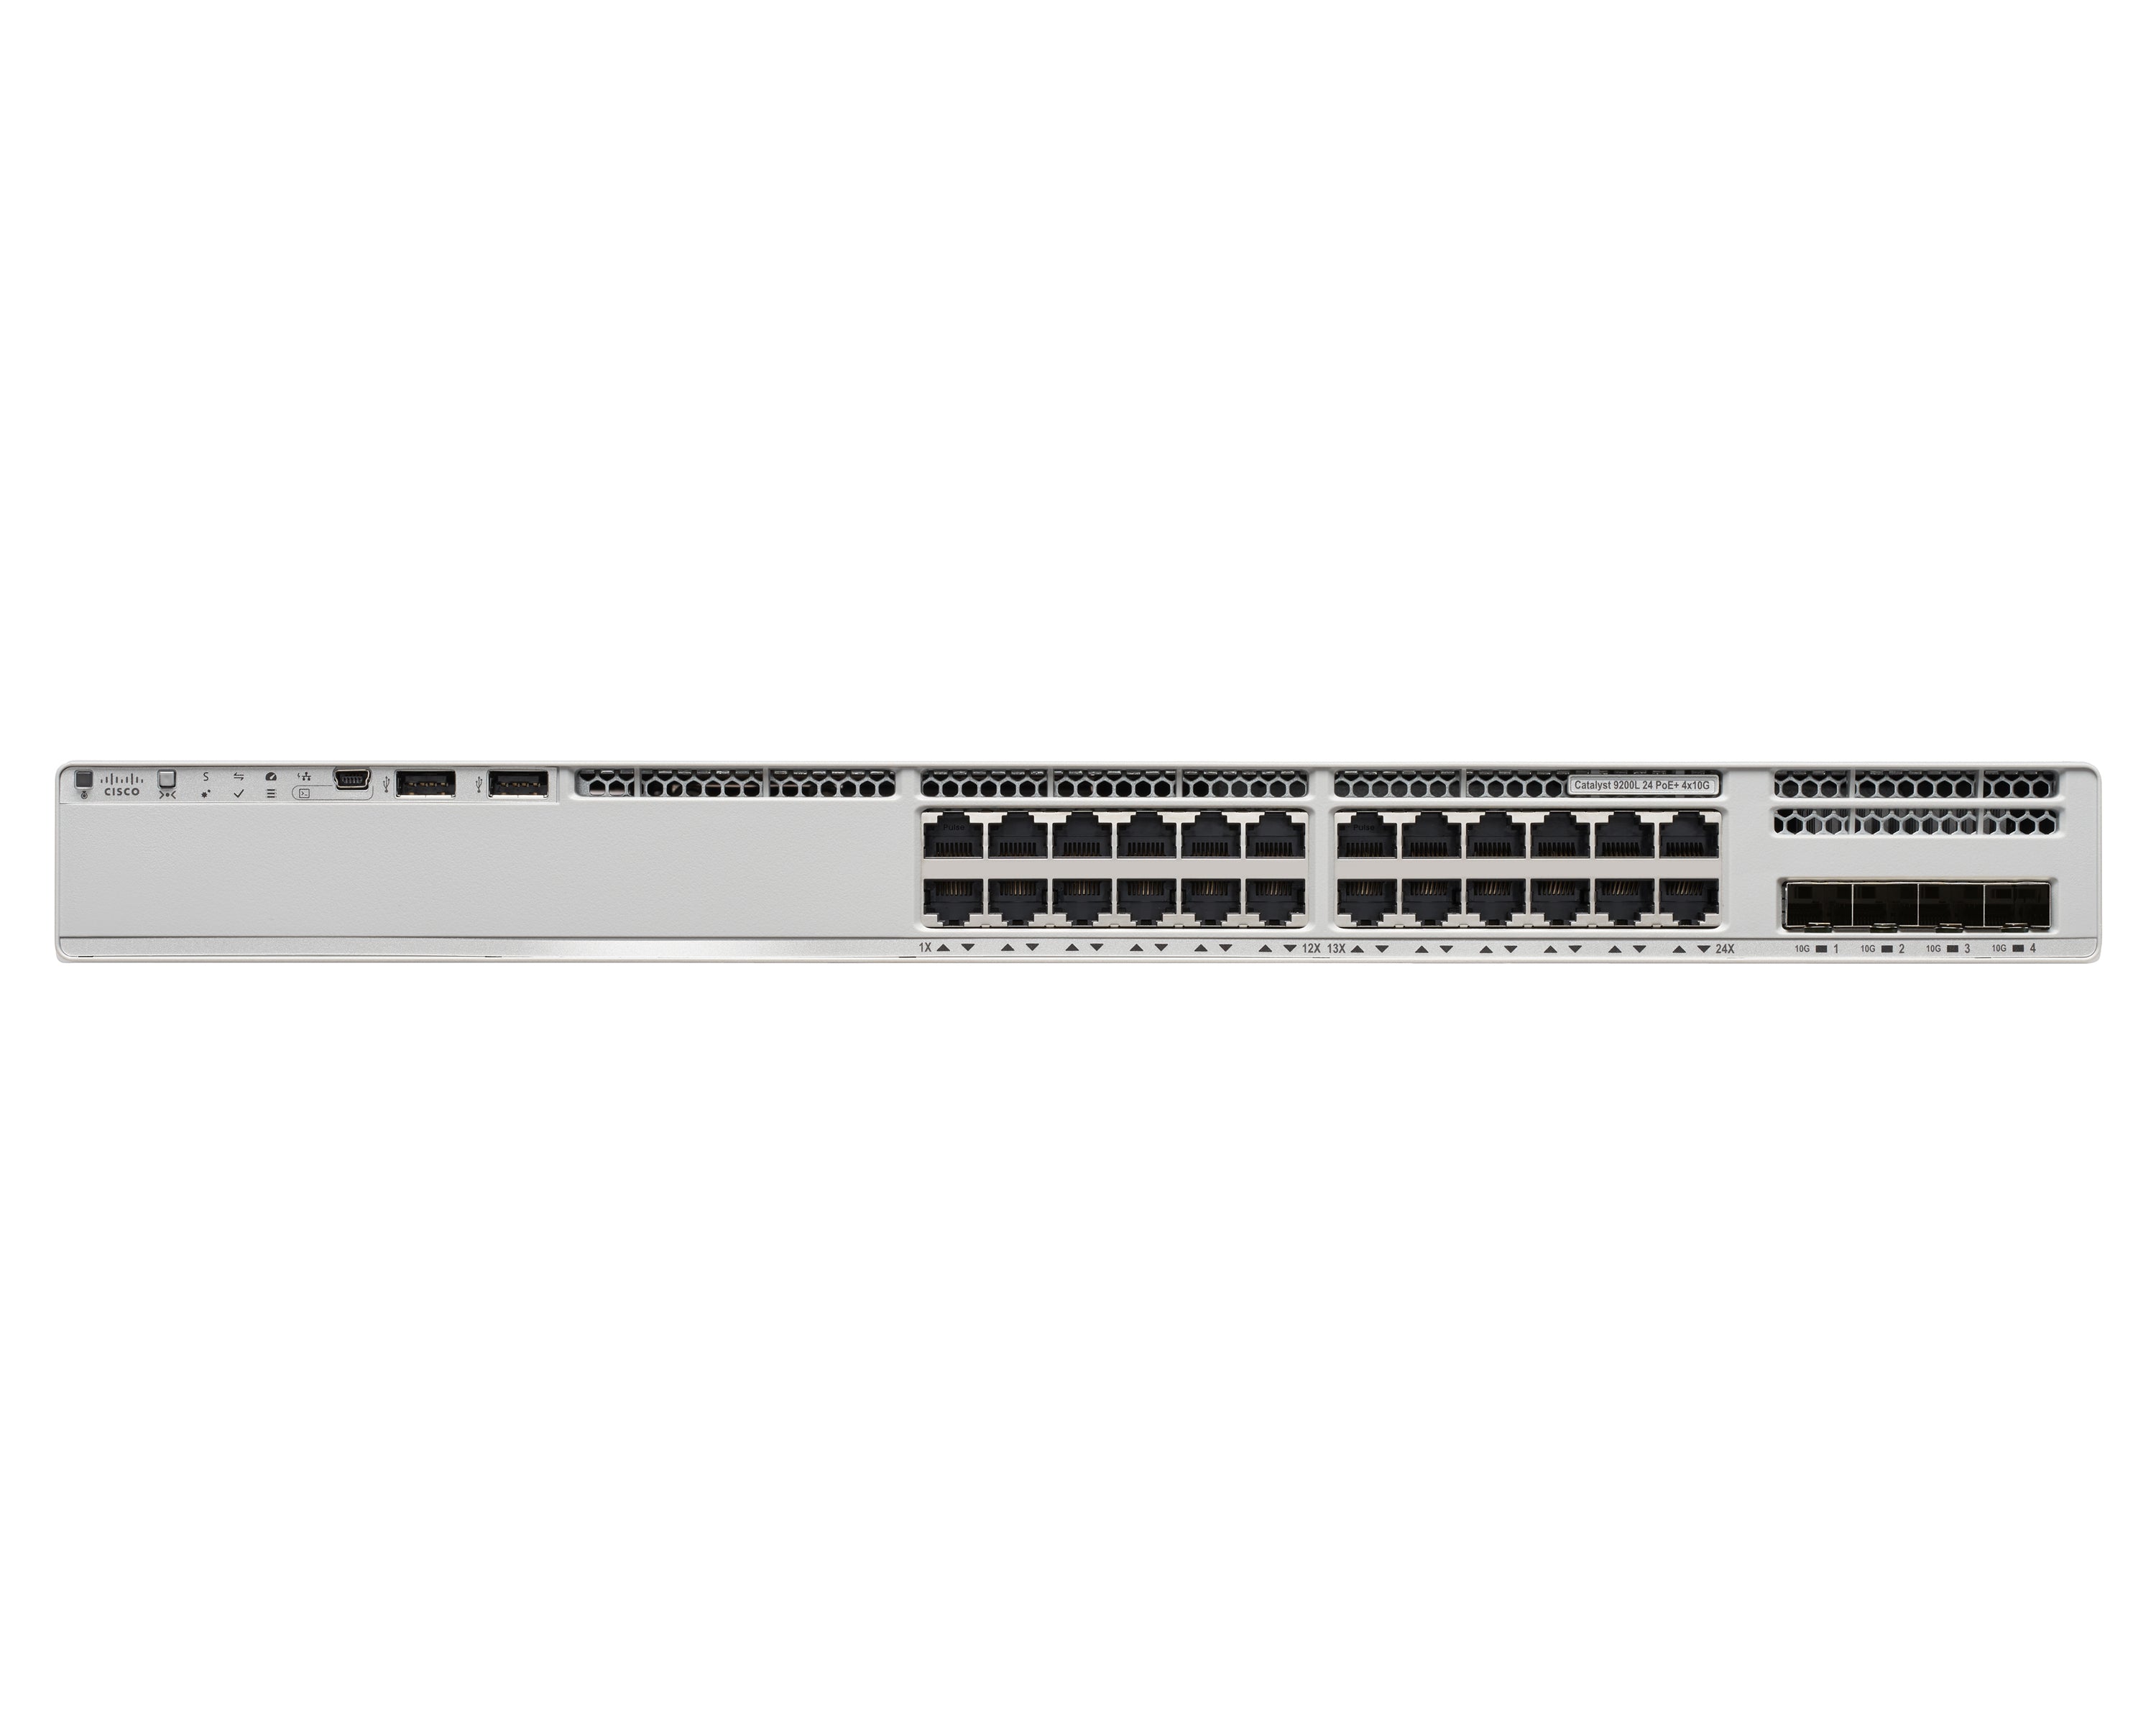
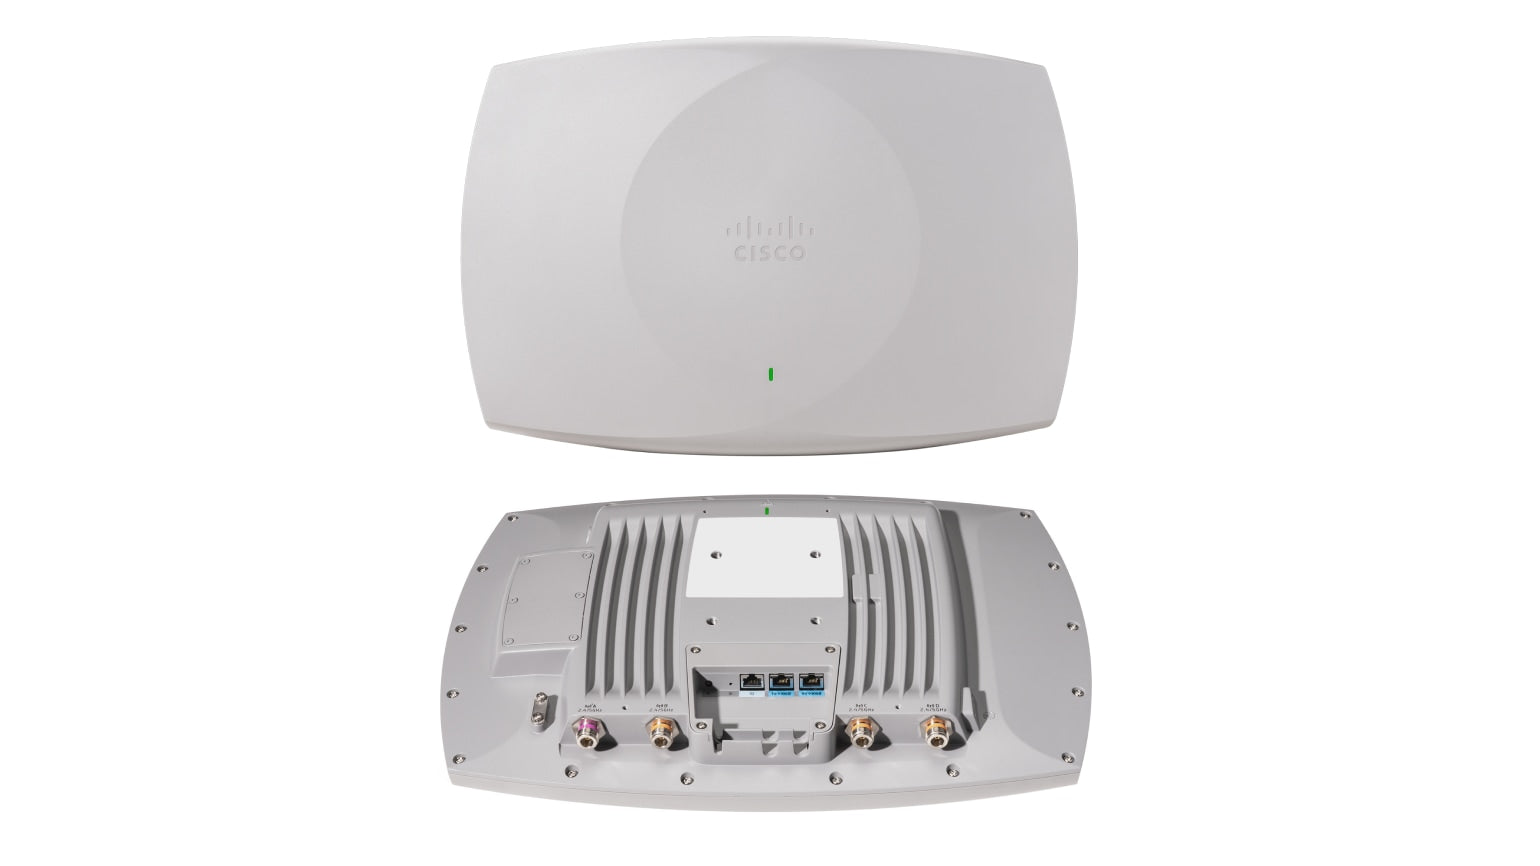
Meraki makes segmentation straightforward. Using Meraki MS switches and MR access points, you can build isolated VLANs that enforce zero trust at the segment level:
- ✓ Employee VLAN — authenticated domain users with access to business applications
- ✓ Guest VLAN — internet-only, fully isolated from internal resources
- ✓ IoT VLAN — printers, cameras, smart devices with no access to business systems
- ✓ Server VLAN — restricted access, only from authorized endpoints and roles
- ✓ Compliance VLAN — PCI/HIPAA scoped traffic with full logging and access controls
Meraki's Group Policy feature lets you assign bandwidth, firewall rules, content filtering, and VLAN placement to any user, device type, or Active Directory group automatically — no manual ACL configuration required.
Visibility: You Can't Trust What You Can't See
Zero trust requires continuous monitoring. If you don't know what's on your network, you can't enforce policy. Meraki's cloud dashboard gives you complete, real-time visibility:
- ✓ Device inventory — every connected device is automatically identified, profiled, and logged
- ✓ Traffic analysis — see what applications every device is using, in real time
- ✓ Rogue device alerts — be notified immediately when an unknown device connects
- ✓ Security event logs — every blocked threat, policy violation, and anomaly is recorded and searchable
- ✓ Syslog and API export — feed Meraki event data into your SIEM or SOC for centralized analysis
This isn't passive logging — Meraki surfaces the data you need to act. The Meraki dashboard flags unusual traffic patterns, unauthorized connection attempts, and policy violations as they happen.
Secure Remote Access That Doesn't Compromise Trust
The shift to hybrid work created a massive attack surface expansion. Employees connecting from home networks, coffee shops, and airports are exactly the scenario zero trust was designed for.
Meraki's Client VPN and Meraki Systems Manager (SM) combine to deliver zero trust remote access:
- ✓ Device posture checks — SM verifies that a device is encrypted, patched, and compliant before it connects to VPN
- ✓ Certificate-based authentication — no password sharing; devices authenticate with certificates managed by SM
- ✓ Split tunneling control — force business traffic through the Meraki MX while keeping personal traffic local
- ✓ Automatic VPN failover — if one MX is unreachable, the client connects through another automatically
Remote workers get the access they need. Your network stays segmented. And every connection is authenticated, encrypted, and logged.
Cisco Talos: Threat Intelligence That Never Sleeps
Zero trust isn't just about what's on your network now — it's about staying ahead of what's coming. Every Cisco Meraki MX includes access to Cisco Talos threat intelligence: one of the world's largest commercial threat research teams, processing over 600 billion security events daily.
Talos continuously updates Meraki's IPS signatures, AMP definitions, and URL reputation databases — automatically, with no manual patching required. When a new ransomware family emerges or a zero-day vulnerability is disclosed, Meraki blocks it before most IT teams have had a chance to read the advisory.
How Novbox Helps You Get There
Zero trust is a journey, not a product. Most SMBs have the hardware foundation already — Meraki equipment is zero-trust-capable out of the box. What they lack is the configuration and policy design to actually enforce it.
Novbox specializes in designing and deploying zero trust environments on Cisco Meraki for U.S. businesses. Our team handles:
- ✓ Network segmentation design and VLAN implementation
- ✓ Identity-based access policies tied to Active Directory or Okta
- ✓ IDS/IPS, AMP, and content filtering configuration
- ✓ Secure remote access with device posture enforcement
- ✓ Ongoing monitoring, alerting, and incident response
Whether you're starting from scratch or hardening an existing Meraki deployment, Novbox gives you enterprise-grade security at SMB-friendly pricing — because zero trust shouldn't be out of reach for businesses without a full security team.
Since deploying Meraki security appliances, we have blocked over 10,000 threats per month automatically. Our team sleeps better at night knowing the network defends itself.
Why Businesses Trust Meraki Security
Enterprise-grade threat protection that deploys in minutes and manages itself from the cloud.
Advanced Threat Protection
Next-gen firewall with intrusion detection, malware filtering, and Cisco Talos threat intelligence built into every MX appliance.
Learn More ›Automated VPN
Site-to-site and client VPN configured in clicks, not hours. Auto VPN creates secure tunnels between locations with zero manual configuration.
Learn More ›Content Filtering
Granular web filtering, geo-IP blocking, and application-layer controls keep your network safe and compliant without extra hardware.
Learn More ›The Power of the Meraki Dashboard
At the heart of Cisco Meraki is an intuitive cloud dashboard that unifies wireless, switching, security, and IoT management into a single view. IT teams can manage their entire distributed infrastructure from anywhere.
- Real-time visibility into network health and client connectivity
- AI-powered analytics that predict issues before they impact users
- Automated firmware updates and security patching
- Role-based access control and audit logging

We replaced three separate security vendors with one Meraki MX appliance per site. Simpler to manage, better protection, and half the cost.
Featured Security Products
Protect your network with these Cisco Meraki security appliances.
Seamless Integration with Your IT Stack
Meraki works alongside the collaboration, security, and productivity tools your team depends on.
- VPN integration with major identity providers
- SAML and RADIUS authentication support
- MDM and endpoint management compatibility
- Open APIs for custom automation workflows
Ready to simplify your network?
Discover how Cisco Meraki cloud-managed networking can transform your business IT infrastructure.
Contact Us